ISO 20000 Certification: Prerequisites, Process, and Cost
ISO 20000 certification means two different things depending on who is asking. One is an audit of your organization against ISO 20000. The other is an exam that one person sits.
Search results mix the two together, and teams lose weeks to it. A service desk manager hunting a company certificate lands on a training catalog. They book a course nobody needed.
In this blog, you will:
Tell organizational certification apart from individual qualification.
See what has to be in place before a Stage 1 audit.
Follow the audit stages and the three-year cycle.
Work out what drives the cost and the timeline.
You will finish able to scope the project and brief a certification body.
What Is ISO 20000 Certification?
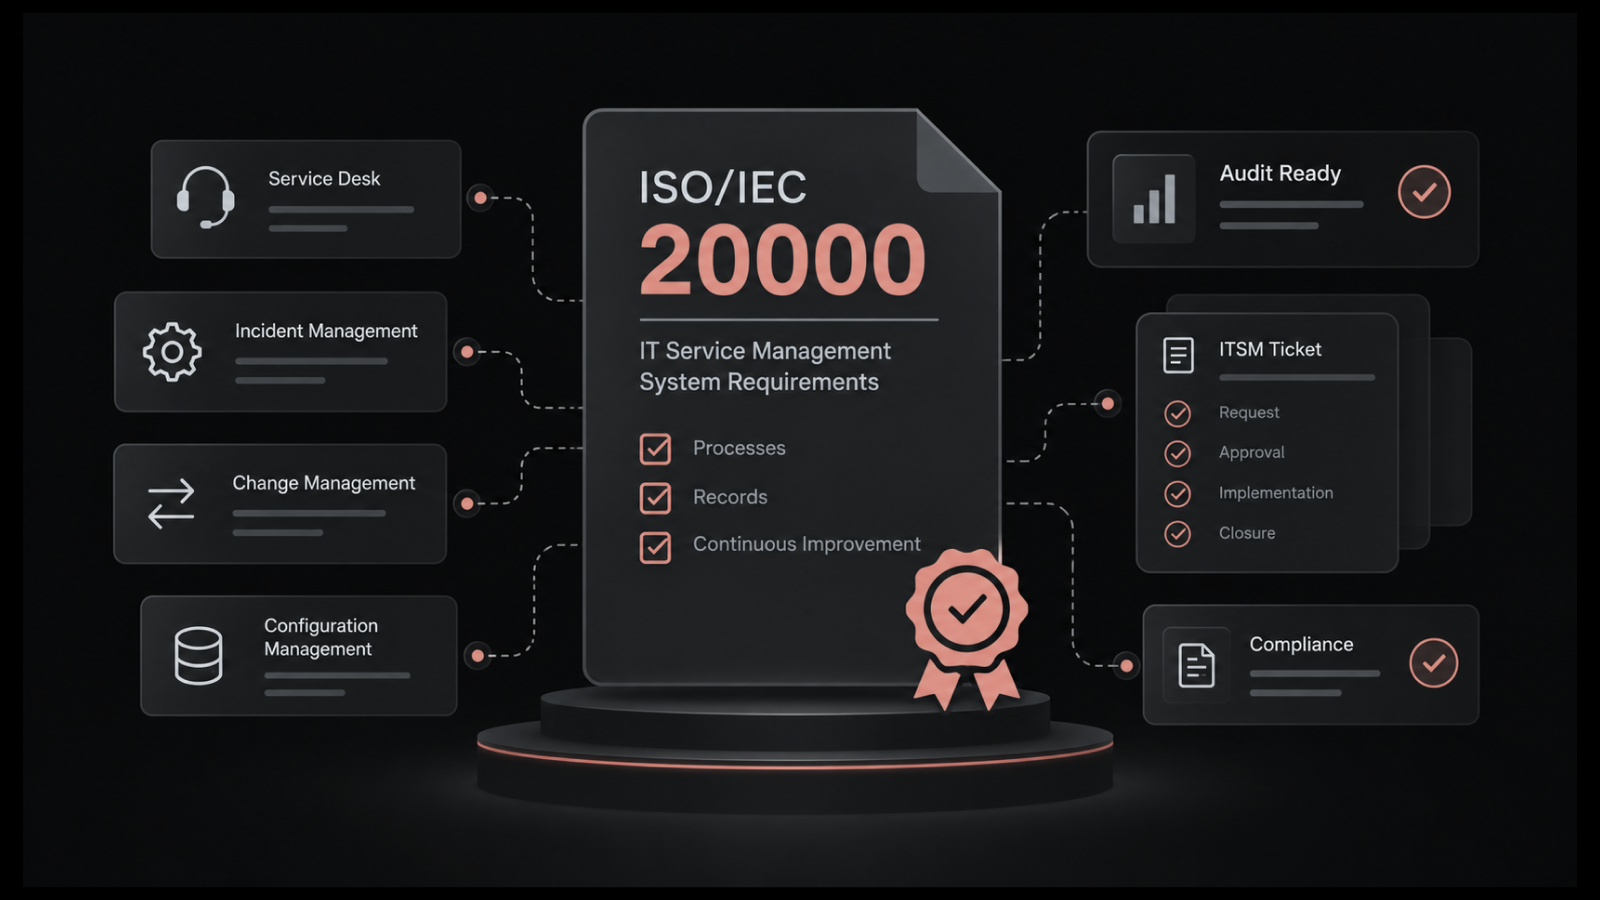
ISO 20000 certification is formal proof from an accredited certification body that your service management system (SMS) meets ISO/IEC 20000-1:2018. An auditor examines how you run IT services. They issue a certificate when you conform.
The certificate belongs to the company and names a defined scope of services. It runs on a three-year cycle. It does not extend to a parent company or a sister business unit.
It does not rate your services. The certificate confirms the system works as written. It says nothing about whether your availability is any good.
Organization Certification vs Individual Certification: Which Do You Need?
Two schemes share the name ISO 20000 certification, and they do not overlap at all. One certifies a company. The other certifies a person.
Organizational certification is what a customer means when they ask whether you are certified. An accredited body audits your SMS. The certificate then names your organization and the services in scope.
Individual qualification is a training credential. A person sits an exam with a training provider. They receive a personal certificate showing they understand the standard. It says nothing about their employer.
Organization certification | Individual qualification | |
What it certifies | Your SMS | One person's knowledge |
Who issues it | An accredited certification body | A training provider |
How you get it | A two-stage audit | An exam |
Named on the certificate | Your organization and its scope | The individual |
Renewal | Three-year cycle with annual checks | Varies by scheme |
Satisfies a customer requirement | Yes | No |
Whatever triggered your search often tells you which one you need. A contract clause or a tender question points to company certification. A job description or a development plan points to the exam.
People leading a rollout often take the individual qualification first. We rate that a sound move. It teaches the standard quickly and shortens the project. It just leaves the company uncertified. Nobody should report it upward as progress against a customer promise.
What You Need Before You Start
Seven things have to exist before a certification body will schedule Stage 1. Most teams we work with have four or five already, and they underestimate the rest.
A defined scope: a written statement of which services, sites, and teams the certificate covers. Include the reasoning behind the boundary.
Named ownership: top management buy-in on record, plus a named owner for the SMS.
A service catalog: the services in scope, written down, with owners against each one.
Service level agreements: targets defined for the services in scope, plus reporting that shows performance.
A configuration management database: the items, their links, and evidence you check the data often.
Operating history: enough months of live records for an auditor to sample across. A system switched on last week has nothing to show.
One completed internal audit and management review: both, finished, with findings and actions recorded.
That last item delays more projects than any other. Clauses 9.2 and 9.3 want an internal audit program and management reviews.
A company that has never audited itself cannot show conformity, however well its service desk runs.
The same trap catches SLAs and OLAs. Agreeing targets is quick. Producing twelve months of reports against them is not. Once the audit is booked, no amount of effort compresses that.
How Does the ISO 20000 Certification Process Work?
Certification runs as nine steps, and the external audit is only the middle of it. The work before Stage 1 takes far longer than the audit itself.
Step | What happens | Who runs it |
1. Gap analysis | Compare current practice against the requirements and list what is missing. | You, or a consultant |
2. Implementation | Build the missing processes, documents, and reporting. | You |
3. Operate and gather records | Run the system long enough to produce evidence an auditor can sample. | You |
4. Internal audit | Audit yourself against every clause and record the findings. | You, or an external auditor |
5. Management review | Top management reviews performance and records decisions and actions. | You |
6. Stage 1 audit | The auditor reviews your documented system and judges whether you are ready. | Certification body |
7. Stage 2 audit | The auditor tests whether you genuinely operate what you documented. | Certification body |
8. Certification decision | An independent reviewer inside the body decides, then issues the certificate. | Certification body |
9. Surveillance and recertification | Annual surveillance audits, then a full recertification audit in year three. | Certification body |
Splitting those nine steps by who owns them shows where the effort really sits.
Steps 6 and 7 deserve a closer look. Teams routinely misread what each one is for.
What Happens in Stage 1
Stage 1 checks your documents for readiness. The auditor reads your scope statement, your policy, and your process documents. They also read the records from your internal audit and management review.
They are answering one question. Is there enough here for a Stage 2 audit to be worth running? A Stage 1 that surfaces gaps ends with a fix list and a delayed Stage 2. We see that outcome often, and it does not count as a failure.
What Happens in Stage 2
Stage 2 tests operation. The auditor samples real records across the clauses and interviews staff. They check whether the documented process matches what people do.
Findings come out as major or minor nonconformities. A minor one gets a corrective action plan and a deadline. A major one blocks the certificate until you fix it and the auditor verifies the fix.
How Long Does ISO 20000 Certification Take?
Most first certifications we see take six to twelve months from gap analysis to certificate. Four things decide where you land in that range. Only one of them sits with the certification body.
The table shows what pulls each factor faster or slower.
Factor | Faster if | Slower if | Who controls it |
1. What already exists | A documented service desk with live SLA reporting | Email, shared mailboxes, and spreadsheets | You |
2. Scope | Two services at one site | Twenty services across four countries, each needing its own catalog entry and targets | You |
3. Evidence history | Months of live records already behind you | A service management system switched on recently | Nobody |
4. Audit scheduling | Stage 1 passes cleanly | Stage 1 raises gaps, so Stage 2 slips by weeks | Certification body |
Factor three sets a floor that nothing compresses. You need enough months of operating records for the auditor to sample.
You also need a finished internal audit and management review cycle. That work runs in calendar time, whatever your headcount.
Teams that miss their target date almost always miss it there. We have never seen documents be the bottleneck.
How Much Does ISO 20000 Certification Cost?
Four separate costs make up an ISO 20000 certification budget. The largest one rarely appears in a quote.
1. Certification Body Audit Fees
The body charges by audit day. It works out how many days Stage 1 and Stage 2 need. Two inputs drive that number: your effective number of personnel, and how complex your scope is. Accredited bodies follow set audit duration rules to do the sum.
Interrogate this number. Ask every body to show the audit-day calculation behind its quote. Two quotes that look far apart often differ on assumed headcount or scope, not on the day rate.
2. Consultancy
Consultancy is optional, and it helps most when nobody internally has run a management system before. A consultant often runs the gap analysis and shapes the documents. Then they hand operation back to you.
A consultant can write your process documents. They cannot make your team run them, and Stage 2 tests exactly that.
3. Training
At minimum, whoever runs your internal audit needs to know how to audit against the standard. Some teams send one person for an individual qualification. That person becomes the project's knowledge base.
4. Internal Effort
We find this is the biggest cost, and almost nobody budgets it. Building the service catalog eats weeks. So do defining targets, reconciling a CMDB, and running an internal audit.
Counting that time changes the business case honestly. A project that looks like an audit fee is often several person-months of service desk work. The fee sits on top.
Two ongoing costs follow certification as well. Surveillance audits recur every year. A full recertification audit falls in year three, so the budget spans three years.
How to Choose an Accredited Certification Body
Accreditation and certification sit on two different layers. Confusing them is how companies end up with a worthless certificate. A certification body audits you. An accreditation body audits that body in turn.
Accreditation bodies belong to the International Accreditation Forum. UKAS covers the United Kingdom, and ANAB covers the United States.
A certificate counts as accredited when its issuing body holds IAF-member accreditation for that exact standard.
According to ISO's analysis of the ISO Survey, 89 countries held accredited ISO/IEC 20000-1 certificates in 2021.
Five checks separate a body worth using from one worth avoiding.
Confirm the accreditation exists: check the public directory, or IAF CertSearch. A logo on a website proves nothing.
Confirm it covers ISO/IEC 20000-1: accreditation is granted per standard. A body accredited for ISO 9001 alone cannot issue an accredited ISO 20000 certificate.
Ask for the audit-day calculation: a body that hides its working cannot defend its number.
Ask about sector experience: an auditor who has assessed service providers like yours reads evidence faster.
Check the surveillance schedule up front: annual audit dates land in your calendar for three years. Agree them before you sign.
What Evidence Do Auditors Ask For?
Auditors sample records instead of reading policies. So the practical question is what your systems can produce on request. The table lists what gets asked for most often.
Area | Evidence the auditor samples |
Scope and context | Scope statement, interested parties analysis, and the climate change assessment added in 2024 |
Leadership | Signed service management policy, named roles, and evidence of management involvement |
Service level management | SLA definitions, performance reports over time, and records of what followed a breach |
Incident and request | Ticket history with classification, priority, timestamps, and resolution detail |
Change management | Change records showing request, assessment, approval, and outcome |
Configuration management | CI records, relationships, and the history of verification activity |
Performance evaluation | Internal audit reports, service reports, and management review minutes with actions |
Improvement | Nonconformity records, corrective actions, and evidence they were closed |
Every row assumes the record was created as the work happened. Reconstructed evidence shows up to an experienced auditor, because timestamps cluster and the detail thins out.
The platform running your service desk decides how hard the audit gets. Motadata ServiceOps produces these records inside the modules that do the work. Incident management, change, release, and knowledge workflows align to ITIL 4.
Audit trails attach to each. SLA performance reporting covers another row. A unified CMDB shared with asset management covers one more, with no separate export step.
Where Certification Attempts Usually Fail
Nonconformities repeat across companies. The same six account for most delayed certificates in the projects we have watched.
1. The Internal Audit Never Happened
Teams treat internal audit as a formality and skip it. Others run it so narrowly that whole clauses go unexamined. Clause 9.2 asks for a planned program covering the whole system. An auditor checks the plan as well as the results.
2. Management Review Left No Records
A conversation in a leadership meeting does not satisfy Clause 9.3. The review needs an agenda covering the required inputs, plus minutes showing decisions and owners.
3. SLA Targets Exist but Nobody Reports on Them
Defining targets and never producing performance reports draws findings constantly. The standard says monitor and report, so the reports become the evidence.
4. The CMDB Was Never Verified
A configuration database populated once and left alone drifts within months. Auditors ask when you last checked the data. They also ask what you did about the gaps.
5. Changes Closed Without Recorded Approval
Emergency changes cause this more than anything. A process that allows verbal approval needs a documented route for capturing it afterwards. Without one, the record shows an unapproved change.
6. The Scope Statement Does Not Match Reality
Scope written early and never revisited stops describing the organization. A service running outside the written boundary draws a finding on the scope itself.
Where to Start Your Certification Project
Start with a gap analysis against Clauses 4 through 10. Do it before you contact a certification body. A body can quote accurately only once you know your scope. The gap analysis is what sets that scope.
Then look at what your current tooling already produces. Prerequisites that a platform generates on its own are close to free. Prerequisites needing a new manual routine are where the months go.
Teams running on spreadsheets and shared mailboxes hit this hardest. One ITSM and observability platform usually closes more prerequisites than any documentation exercise. The catalog, the SLA reporting, and the configuration data stop being three projects.
Scope the Project Before You Call a Certification Body
ISO 20000 certification gets won in the months before the auditor arrives, not during the audit. The teams that pass first time are the ones whose service desk was already producing the evidence. The audit simply found it.
The honest difficulty is calendar time. Records have to build up. An internal audit has to run, and management has to review the results. None of that compresses under pressure.
Work out your scope first. Count what your current tools already produce, and treat the rest as the project. That order also makes choosing an ITSM solution easier. The gaps tell you what the platform has to cover.
FAQs
How long is an ISO 20000 certificate valid?
A certificate stays valid for three years. Surveillance audits run every year to confirm the system still operates. A full recertification audit falls in year three, and missing a surveillance audit can suspend the certificate.
Can a small IT team get ISO 20000 certified?
Yes, and audit duration scales with your effective number of personnel and scope. A small team pays for fewer audit days. The requirements do not change, but the evidence volume is far smaller.
What happens if you fail the Stage 2 audit?
You receive nonconformities instead of a pass or fail verdict. Minor ones get a corrective action plan with a deadline. A major nonconformity holds the certificate until you fix it and the auditor verifies the fix.
Can you get certified without hiring a consultant?
Yes, and many teams do. A consultant helps most when nobody internally has run a management system before. What you cannot outsource is operating the system, since Stage 2 tests what your team really does.
Is ISO 20000 certification mandatory?
No law requires it. It becomes mandatory in practice when customers or tenders ask for it. Managed services and public sector IT contracts drive most of that demand. Check whether your buyers request it before committing.
Author
Ramya Shah
Technical Writer
Ramya Shah is a technical content writer with a computer engineering background and roots in automotive journalism. He covers IT Service Management, observability, IT operations, and AI-driven automation. An early adopter of AI-assisted writing workflows, he turns complex IT processes into clear, engaging content optimized for search and answer engines (AEO), lifting content output and organic visibility.